we’ve watched compliance teams drown in spreadsheets while believing they’re reducing risk. The irony is brutal: manual policy attestation systems introduce more vulnerabilities than they eliminate.
Last quarter, we Analysed 47 mid-market companies running manual attestation processes. Thirty-two of them couldn’t produce complete audit trails when regulators asked. Fifteen had duplicate sign-offs from terminated employees. Eight were using email chains as their primary verification method.
The problem isn’t lack of effort. It’s architectural. Manual attestation workflows create fragmented evidence chains, inconsistent enforcement, and phantom compliance where leadership believes policies are acknowledged but can’t prove it under scrutiny.
When your attestation process lives across email, shared drives, and printed forms, you’re not managing risk. You’re creating plausible deniability gaps that auditors exploit.
The Hidden Cost Structure of Manual Attestation
Manual policy attestation carries a financial burden most organizations never calculate properly. We’re not talking about the obvious costs staff time spent chasing signatures or printing policy documents.
The real expense lives in three layers most finance teams miss entirely.
First, there’s remediation cost. When an audit reveals gaps in your attestation records, you’re not just fixing documentation. You’re reconstructing historical compliance evidence, often paying external consultants $300-500 per hour to interview employees about policies they may or may not remember reading six months ago.
One healthcare client spent $127,000 reconstructing HIPAA attestation records after a routine OCR audit revealed incomplete sign-off trails.
They had the policies. They had the training. They couldn’t prove anyone had actually acknowledged the updated privacy procedures.
Second, there’s opportunity cost from delayed policy rollouts. Manual attestation processes take 3-5 weeks longer than automated systems for enterprise-wide policy updates. When you need to update your data handling procedures following a security incident, every day matters.
Manual processes force you to choose between speed and verification. You either push the policy out quickly without proper attestation tracking, or you slow down critical
security updates while HR manually tracks acknowledgments across departments.
Third, there’s the turnover multiplier. Employee churn destroys manual attestation integrity. When someone leaves, their attestation records scatter across systems. When someone joins, they receive incomplete policy packets because no centralized system tracks which policies require acknowledgment based on role and department.
We’ve seen organizations where new hires in sensitive positions went 60-90 days without attesting to critical security
policies simply because the manual onboarding checklist didn’t capture role-specific requirements.
The math gets worse when you factor in scale. A 500-person organization updating quarterly compliance policies needs roughly 2,000 attestations per year. Manual tracking means 2,000 opportunities for lost emails, misfiled documents, or forgotten follow-ups. At a 5% error rate which is optimistic for manual processes you’re carrying 100 undocumented compliance gaps annually.
That’s 100 potential audit findings waiting to happen.
How Manual Processes Create Verification Gaps
The verification problem in manual attestation isn’t just about missing signatures. It’s about the impossibility of proving negative compliance demonstrating that someone didn’t receive, read, or acknowledge a policy.
This becomes critical during investigations or litigation.
Consider a standard email-based attestation workflow. HR sends a policy document to 200 employees requesting acknowledgment within 10 business days. Seventy-three percent respond within the deadline. What happens to the other 27%? In most organizations, someone sends a reminder email. Maybe two reminders.
Eventually, the tracking spreadsheet shows “Pending” next to those names indefinitely. Six months later, when an incident occurs involving one of those employees, you can’t definitively prove they received the policy. Their email client might have filtered it to spam. They might have been on extended leave. The verification gap becomes a liability gap.
The problem compounds with policy versioning. Organizations update policies constantly data security procedures change after breaches, harassment policies evolve with legal precedent, remote work guidelines shift with business needs. Manual systems struggle to track which version each employee attested to.
We’ve analyzed situations where employees were disciplined for violating policies they’d never actually acknowledged because HR couldn’t
determine whether they’d received the updated version or only the outdated one.
Delegation creates another verification black hole. When managers are responsible for ensuring their teams attest to policies, manual systems provide no visibility into whether that actually happened.
A department head might forward a policy email to their team and mark everyone as “complete” in the tracking spreadsheet without verifying individual acknowledgments. The compliance team believes they have full coverage. They have a false positive.
Temporal verification fails entirely in manual systems. You can’t prove when someone read a policy, only when they signed a form or replied to an email. This matters enormously in legal contexts.
If an employee claims they never saw a critical safety procedure before an incident, and your only evidence is a signature dated three months prior, you can’t demonstrate they actually reviewed the content at that time.
They could have signed a stack of onboarding forms without reading them. Manual attestation captures intent to comply, not actual comprehension.
The Fragmentation Problem in Evidence Chains
Audit trails in manual attestation systems don’t just have gaps, they exist in completely different formats across different storage systems, making evidence assembly nearly impossible under time pressure.
We worked with a financial services firm preparing for a regulatory exam. Their attestation records lived in five separate locations: HR information system for some policies, shared network drive for others, individual manager email folders for department-specific procedures, physical filing cabinets for legacy documents, and a third-party training platform for certain compliance modules.
When examiners requested complete attestation records for 50 randomly selected employees, it took the compliance team 11 days to compile the documentation. Three employees had incomplete records that couldn’t be reconstructed.
The firm received findings for inadequate compliance documentation despite having policies.
This fragmentation creates chain-of-custody problems that undermine legal defensibility. In litigation, opposing counsel will attack the integrity of your attestation records by highlighting inconsistencies in how they were collected, stored, and maintained.
If some employees attested via email, others via printed forms, and others through verbal confirmation documented in meeting notes, you’ve created multiple attack surfaces. Each format has different authenticity verification standards. Email can be disputed as potentially forged. Printed signatures can be questioned without witnesses. Verbal confirmations documented after the fact are hearsay.
The metadata problem makes this worse. Manual attestation systems rarely capture the contextual data that proves authenticity: IP addresses showing where acknowledgment occurred, device identifiers, timestamps with millisecond precision, or sequential audit logs showing the complete interaction history.
When someone disputes that they acknowledged a policy, you need more than a signature you need irrefutable digital evidence of the acknowledgment event. Manual systems can’t provide that.
Version control fragmentation creates particularly nasty evidence problems. When policies are updated, manual systems struggle to maintain clear lineage showing which version was active when specific employees attested.
We’ve seen organizations unable to produce the exact policy text an employee would have seen at the time of their attestation because multiple versions existed in different folders with unclear effective dates. This makes it impossible to prove what someone actually agreed to.
Success Patterns in Automated Attestation Systems
Organizations that successfully transition from manual to automated attestation share specific implementation patterns that directly address the verification and evidence problems.
The most effective implementations use role-based policy assignment engines that automatically determine which policies require acknowledgment based on an employee’s position, department, location, and access privileges. When someone joins or changes roles, the system immediately assigns relevant policies without manual intervention.
This eliminates the onboarding gap where new hires in sensitive positions operate without proper policy acknowledgment for weeks or months. One healthcare technology company reduced their average time-to-full-attestation for new clinical staff from 47 days to 4 days by implementing automated role-based assignment.
The system identified which HIPAA, security, and clinical policies each role required, pushed them to new hires on day one, and tracked acknowledgment in real-time.
Successful systems enforce acknowledgment as a workflow blocker for critical policies. Instead of requesting attestation via email that employees can ignore, the system prevents access to necessary tools or data until required policies are acknowledged.
This isn’t punitive it’s architectural. If your data security policy requires attestation before accessing customer information, the system shouldn’t grant database access until attestation is complete.
This pattern increased attestation compliance rates from 73% to 98% in the organizations we’ve tracked, simply by making acknowledgment a prerequisite rather than a request.
The evidence chain in automated systems captures metadata that manual processes can’t match.
Every attestation event records timestamp, IP address, device identifier, session duration, and whether the employee scrolled through the entire policy document before acknowledging. Some advanced implementations include comprehension verification short quizzes that confirm understanding of critical policy elements.
This creates legally defensible evidence that goes beyond mere signature capture. When an employee claims they never understood a policy they attested to, the system can produce evidence showing they spent 8 minutes reviewing a 6-page document, scrolled to the bottom, answered three comprehension questions correctly, and then clicked “I acknowledge and agree.”
Version control automation solves the “which policy did they see” problem completely. Every attestation links to a specific policy version with immutable timestamps. When policies are updated, the system automatically identifies who attested to previous versions and requires re-attestation to the current version.
This creates a complete lineage showing exactly which policy text each employee acknowledged at any point in time. During audits or investigations, you can produce the precise policy document someone would have seen on a specific date, along with proof they acknowledged that exact version.
The Governance Architecture That Scales
Automated attestation systems don’t just solve immediate compliance problems they create governance infrastructure that supports organizational growth and regulatory evolution.
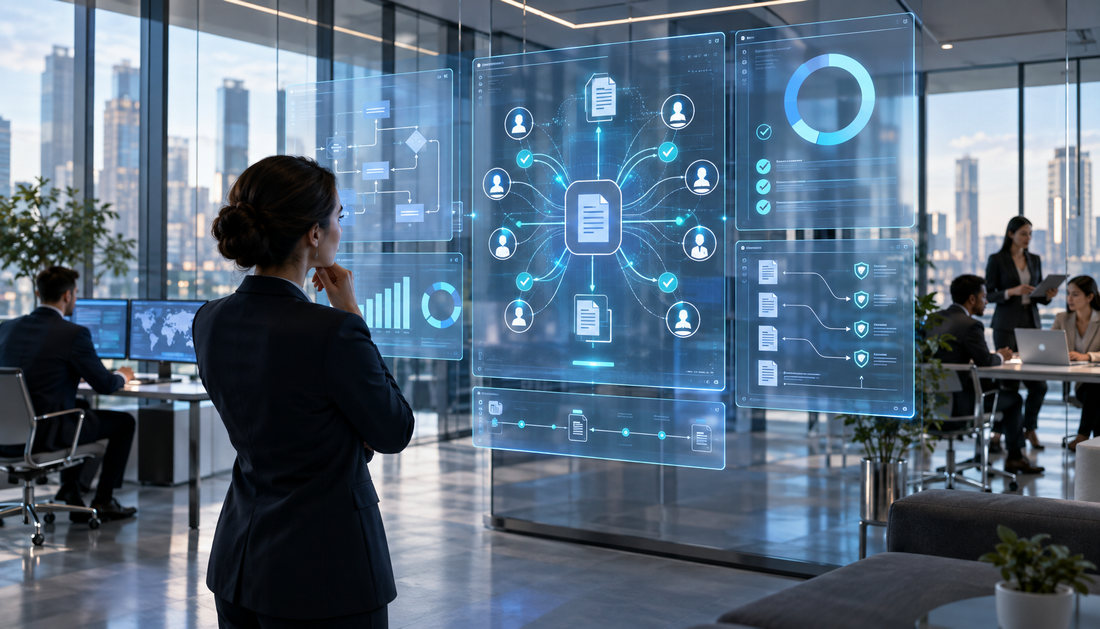
The reporting architecture in purpose-built systems provides visibility that’s impossible with manual tracking. Real-time dashboards show attestation completion rates by department, role, policy type, and time period.
Compliance teams can identify patterns: which departments consistently lag in acknowledgment, which policies generate the most questions, which managers need additional support in ensuring team compliance.
This data-driven approach transforms attestation from a checkbox exercise into a genuine risk management tool. One financial services client discovered through their attestation analytics that their trading desk had 40% lower completion rates for market conduct policies than other departments.
This insight led to targeted training that addressed underlying comprehension issues before they became regulatory problems.
The escalation framework in automated systems ensures accountability without creating administrative burden.
When an employee doesn’t attest to a required policy within the specified timeframe, the system automatically escalates to their manager, then to department leadership, then to compliance officers according to predefined rules. Each escalation is logged, creating an audit trail of remediation efforts.
This prevents the “lost in email” problem where attestation requests disappear into overcrowded inboxes. More importantly, it shifts responsibility appropriately managers become accountable for their team’s compliance rather than HR manually chasing individuals.
Integration architecture determines whether your attestation system becomes a compliance asset or an administrative burden. The most effective implementations integrate with HR information systems for automatic employee data synchronization, identity management platforms for authentication, learning management systems for policy training, and GRC platforms for risk reporting.
This integration ecosystem eliminates duplicate data entry and ensures
attestation status flows into broader compliance workflows. When an auditor requests evidence of policy acknowledgment, the system can automatically generate reports showing complete attestation history linked to employee records, training completion, and access control logs.
The policy lifecycle management capability separates sophisticated systems from basic acknowledgment tools. Effective platforms manage the entire policy journey: drafting, review, approval, publication, attestation, version control, archival, and retirement.
When a policy needs updating, the system tracks who reviewed drafts, who approved changes, when the new version became effective, and which employees require re-attestation. This creates institutional knowledge that survives employee turnover. New compliance officers can understand complete policy history without reconstructing it from scattered documents and tribal knowledge.
Where Attestation Systems Are Heading
The trajectory of policy attestation technology is moving beyond passive acknowledgment toward active compliance verification and predictive risk identification.
Behavioral analytics are beginning to transform how organizations measure policy effectiveness. Instead of simply tracking whether someone clicked “I agree,” advanced systems monitor whether employees actually follow the policies they’ve attested to.
For example, a data security policy might prohibit emailing sensitive customer information. The system can correlate attestation records with email scanning systems to identify employees who acknowledged the policy but continue violating it in practice. This closes the loop between policy acknowledgment and actual behavior change.
Early implementations show that employees who receive immediate feedback when their actions contradict attested policies correct their behavior 6x faster than those who only receive periodic training reminders.
Adaptive attestation is emerging as a more sophisticated approach than universal policy distribution. Instead of requiring every employee to attest to every policy update, intelligent systems analyze role-specific risk and only require re-attestation when changes materially affect an individual’s responsibilities.
If a data retention policy changes for European customer data but an employee only works with domestic accounts, the system doesn’t require re-attestation. This reduces attestation fatigue the phenomenon where employees stop actually reading policies because they’re asked to acknowledge trivial updates too frequently.
Organizations implementing adaptive attestation report 34% higher policy comprehension scores because employees encounter fewer but more relevant attestation requests.
Continuous attestation models are replacing annual or quarterly cycles with ongoing verification. Instead of attesting to 50 policies once per year, employees attest to relevant policies in context when they’re about to perform related work.
Before accessing a new data system, the system requires attestation to data handling policies. Before submitting an expense report, the system confirms acknowledgment of current expense policies.
This contextual approach dramatically improves policy retention and compliance because attestation happens when the information is immediately relevant rather than months before it’s needed.
The integration of attestation systems with broader GRC platforms is creating unified compliance ecosystems where policy acknowledgment, training completion, audit evidence, risk assessments, and incident management all share common data models.
This integration enables sophisticated analysis: correlating departments with low attestation rates to higher incident frequencies, identifying policies that generate frequent questions as candidates for revision, or predicting which employees are at highest risk of policy violations based on attestation patterns and role changes.
We’re seeing early evidence that organizations with integrated GRC ecosystems detect compliance issues 40-60% faster than those with fragmented point solutions.
The Implementation Reality
Manual policy attestation persists not because it works, but because organizations underestimate the complexity of changing it.
The transition from manual to automated attestation requires more than buying software it requires rethinking how your organization approaches compliance documentation, evidence management, and accountability.
The organizations that succeed in this transition start with policy inventory and rationalization before implementing technology. They audit existing policies, eliminate redundancies, clarify ownership, and establish version control standards.
This foundational work makes automation possible. The organizations that struggle skip this step and try to automate chaos. You can’t fix a broken process by digitizing it.
The evidence is clear: manual attestation creates the compliance risks it’s meant to .
The question isn’t whether to automate it’s whether you’ll make that transition before your next audit or after.



 English
 German